Software Supply Chain Security on AWS
A GitHub Actions pipeline that signs a container image keylessly, attaches SLSA provenance, and refuses to call it deployable until both verify against the exact repo that built it.
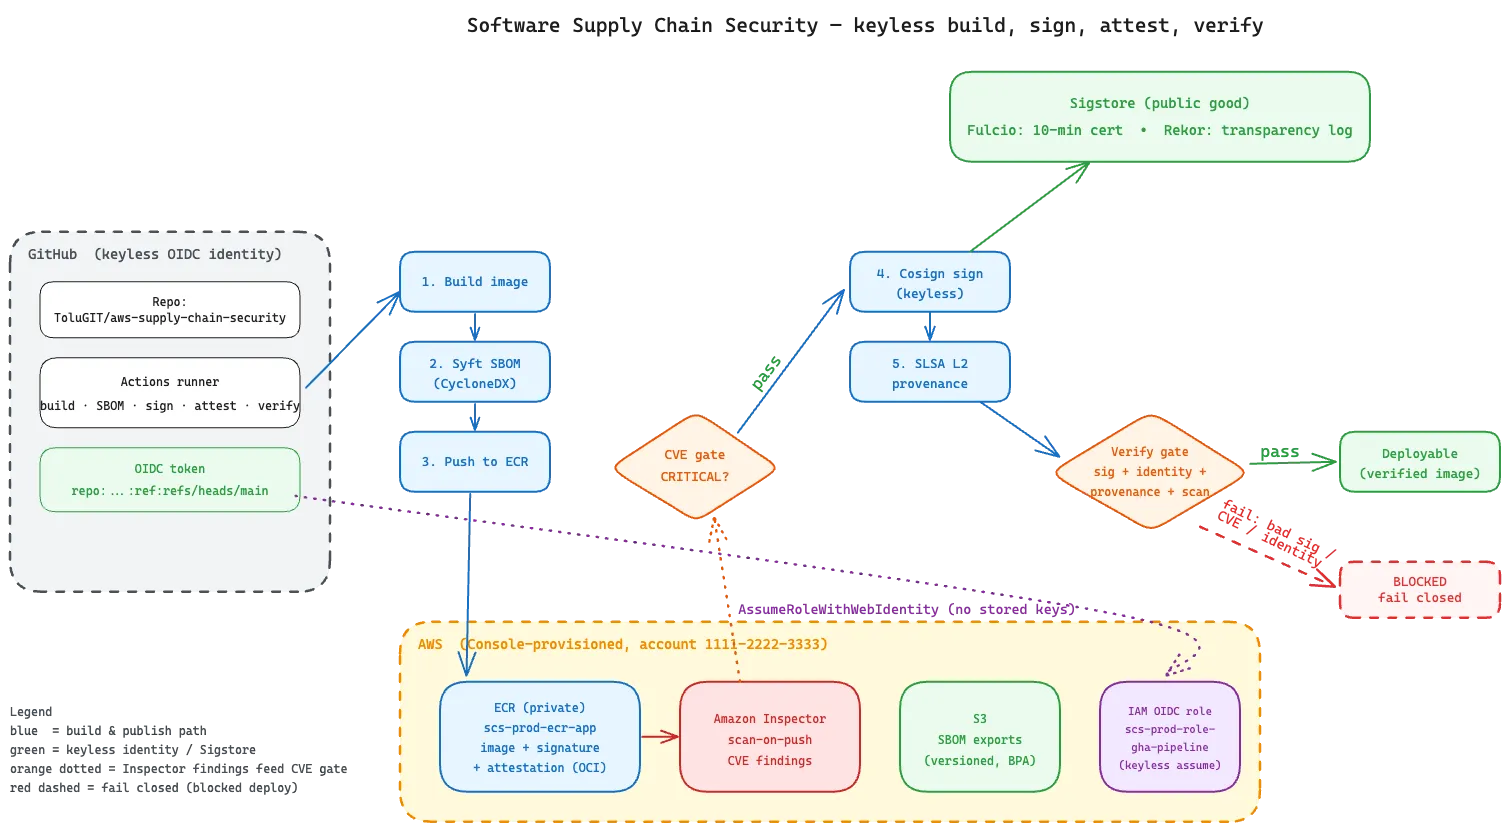
A scanner answers "does this image carry known CVEs right now," not "where did this image come from." An attacker who compromises CI can push a malicious image under a legitimate tag and still get a clean scan.
GitHub Actions builds and pushes the image to ECR. Inspector gates only on fixable CRITICAL and HIGH findings, because the base image ships an unpatchable perl CVE that would otherwise block every build forever. Syft generates an SBOM. Cosign signs the image digest keylessly through Fulcio and Rekor, with no private key anywhere. A SLSA Build L2 provenance attestation records what built it. A verify gate checks the signature, the signing identity, and the provenance together before anything counts as deployable.
Signed, attested, verified, therefore deployable. None of those words alone means anything.
Three adversarial tests proved the controls. A vulnerable image variant with three fixable CRITICALs and seventeen fixable HIGHs was blocked before signing. A tampered image carrying an IMDS credential-exfiltration layer had no valid signature for its new digest. A validly signed image failed verification when pinned to the wrong expected identity, and passed only against the correct one.
- Cosign keyless signing: no private key, a ten-minute Fulcio certificate, logged in Rekor
- CVE gate fires only on fixable findings, catching a fail-open bug that let three CRITICALs through unsigned
- SLSA Build L2 provenance verified against the exact repo, workflow, and ref before deploy